Security Assessment
Comprehensive Security Posture Assessment
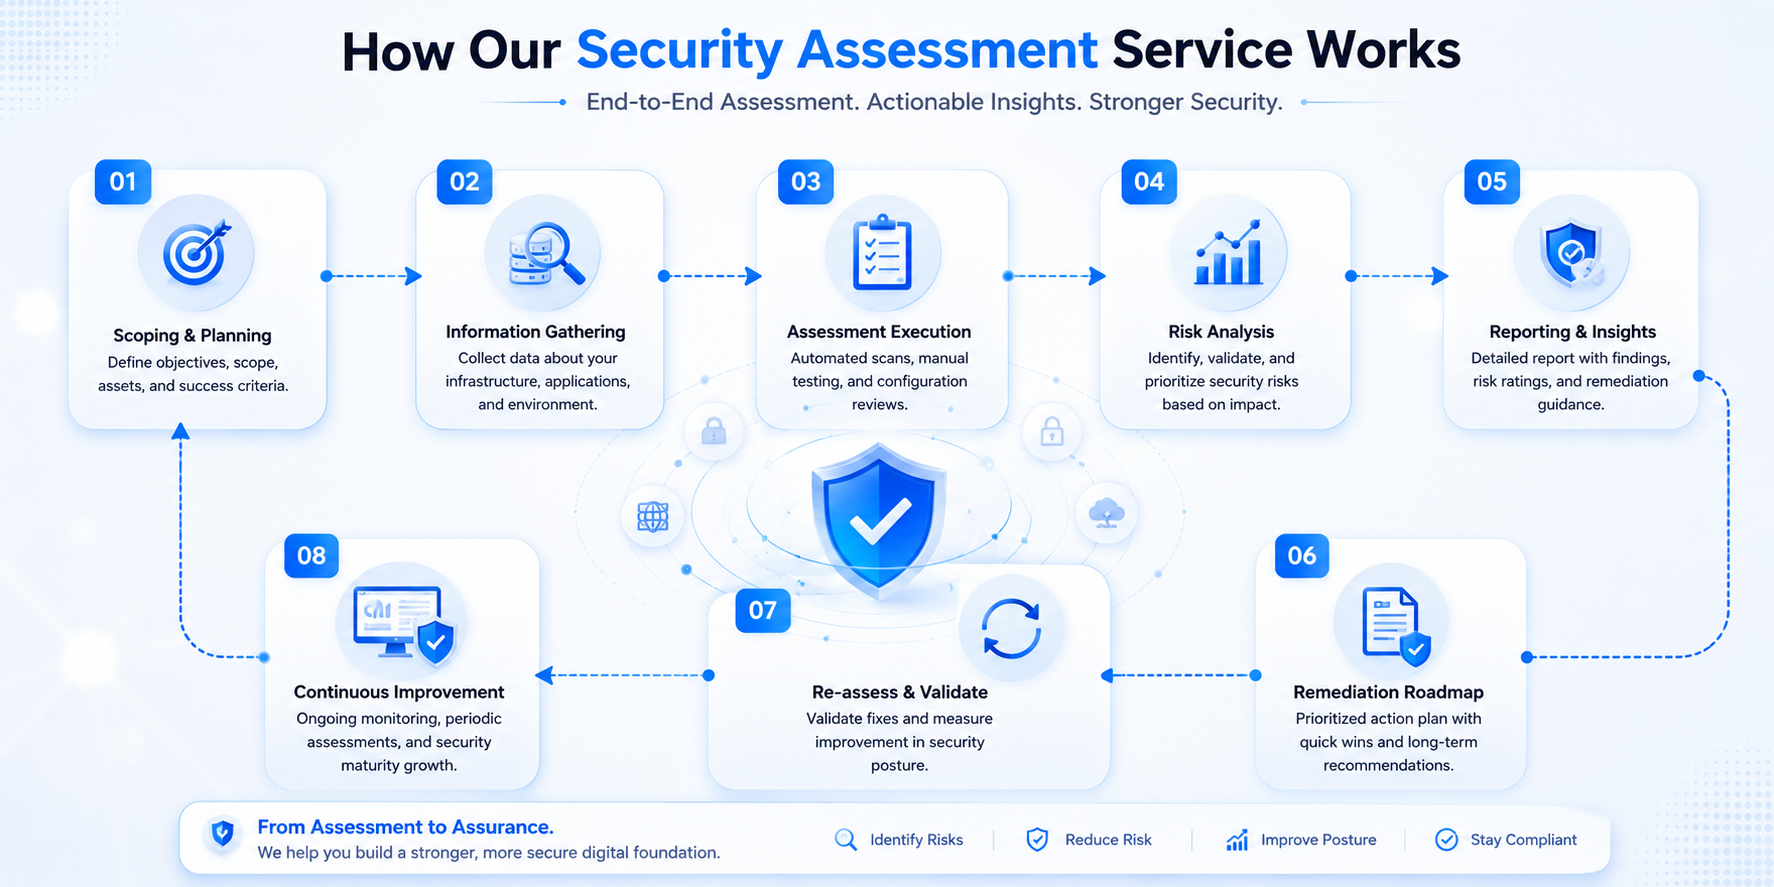
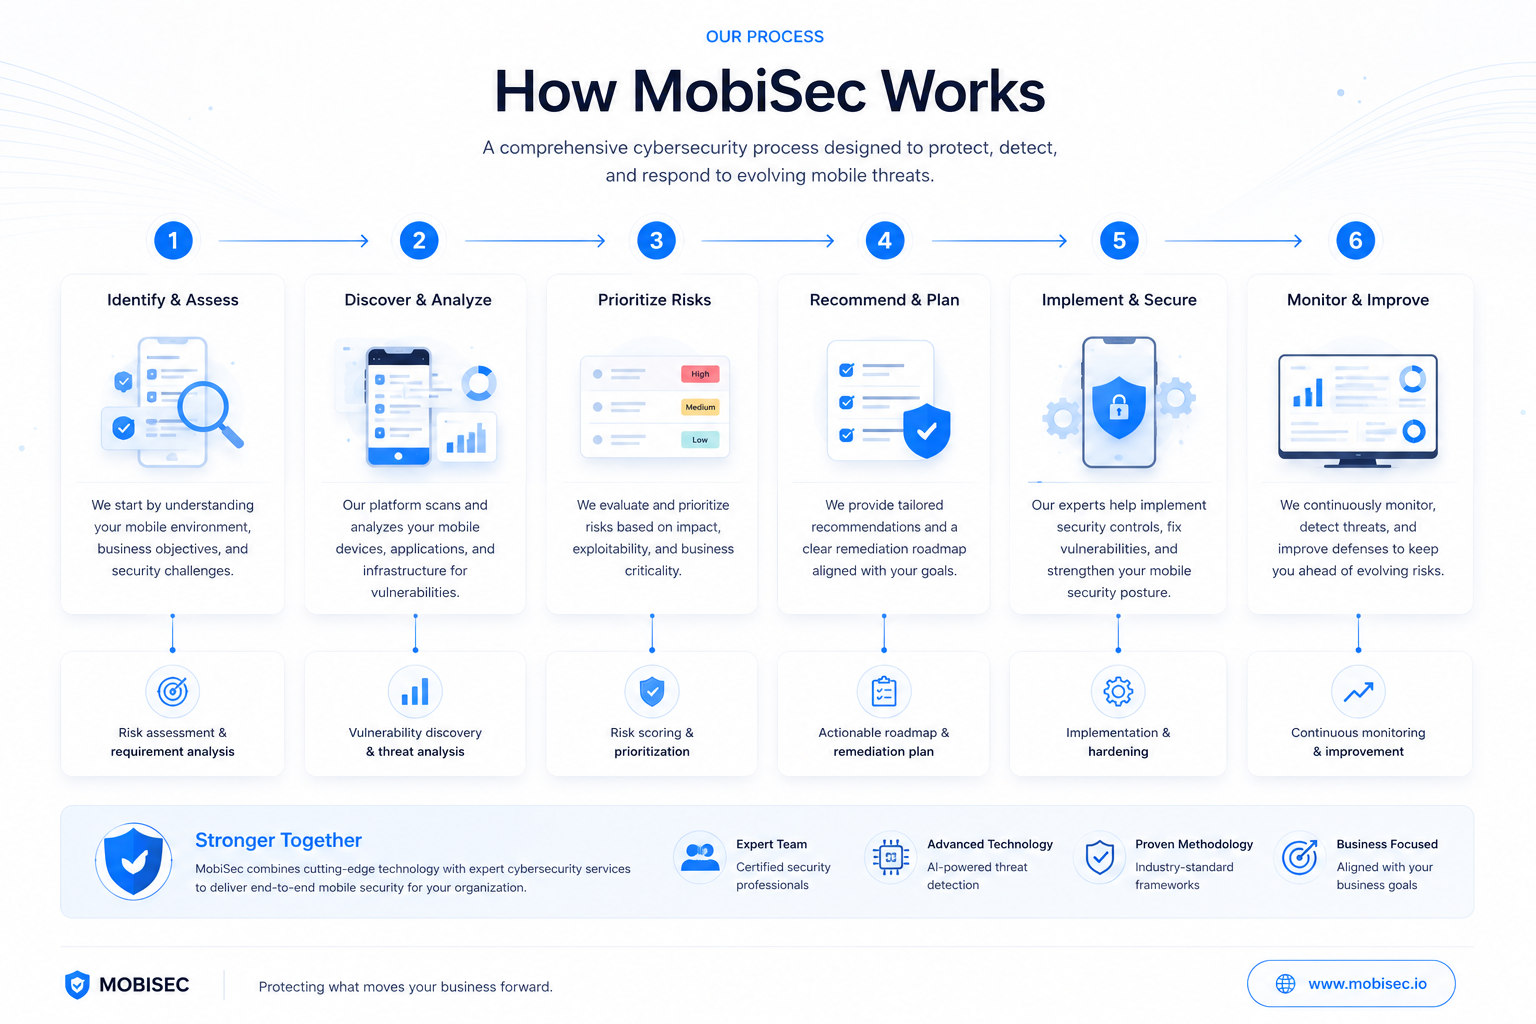
A MOBISEC Cybersecurity Audit delivers a thorough, independent assessment of your organisation's security posture. Our experts analyse your infrastructure, policies, processes, and technology controls to identify vulnerabilities and provide a prioritised remediation roadmap — before attackers find the gaps first.
Security Posture Assessment
Comprehensive evaluation of your organisation's security posture across infrastructure, applications, policies, processes, and security controls.
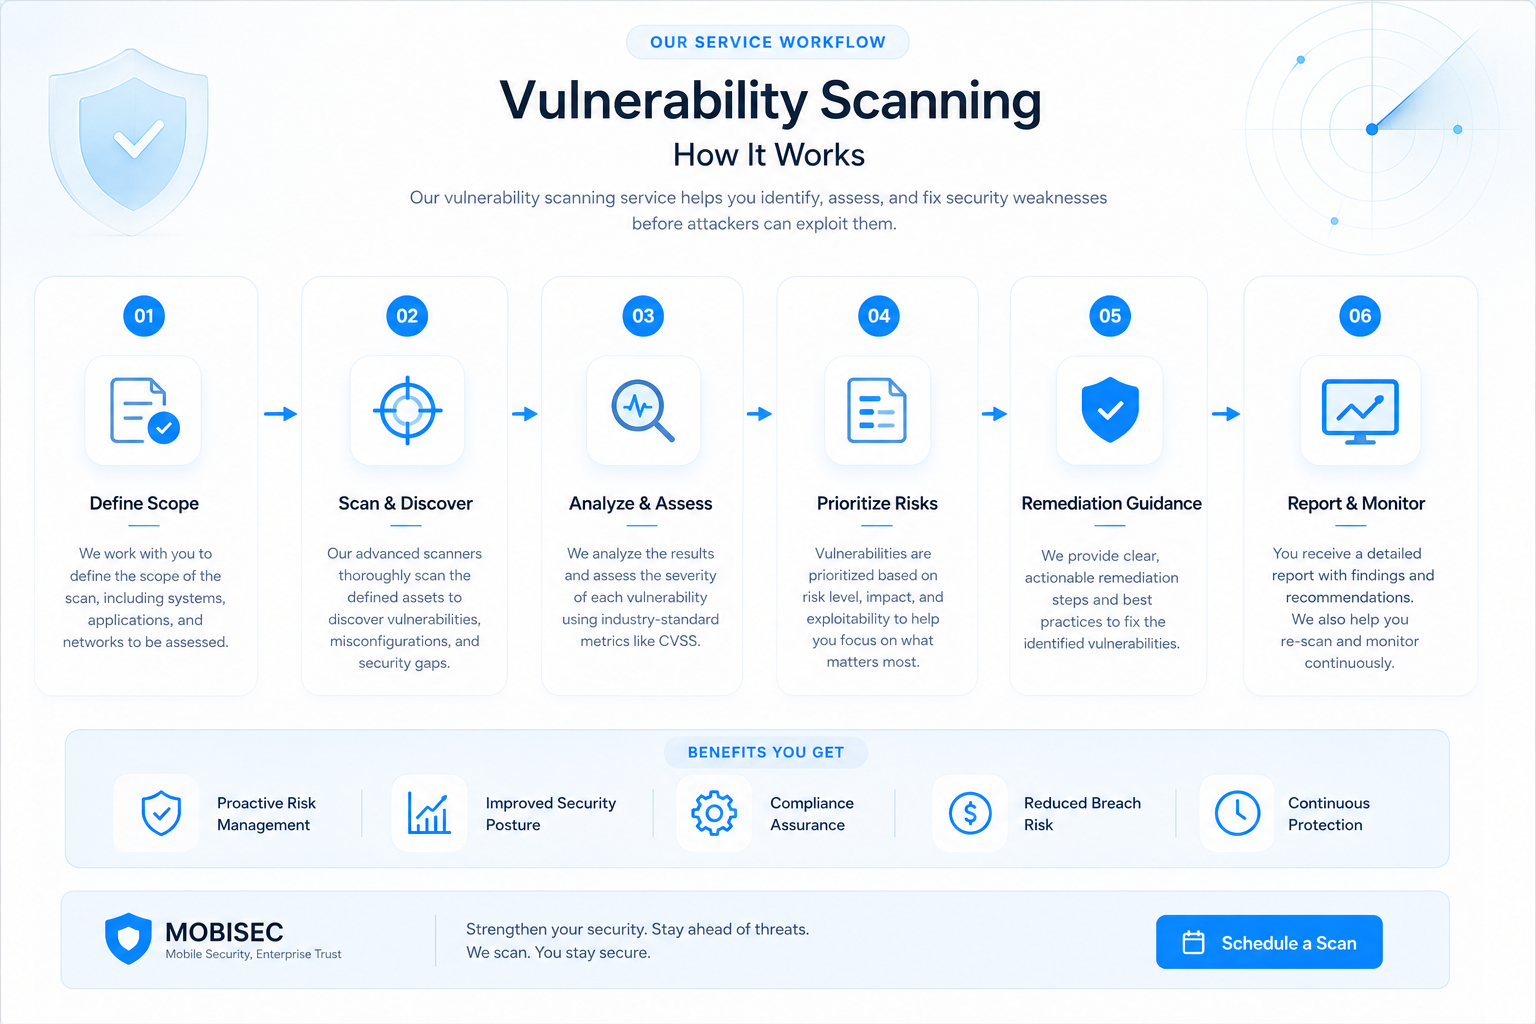
Vulnerability Discovery
Identify security weaknesses, misconfigurations, and exploitable vulnerabilities before attackers can take advantage of them.
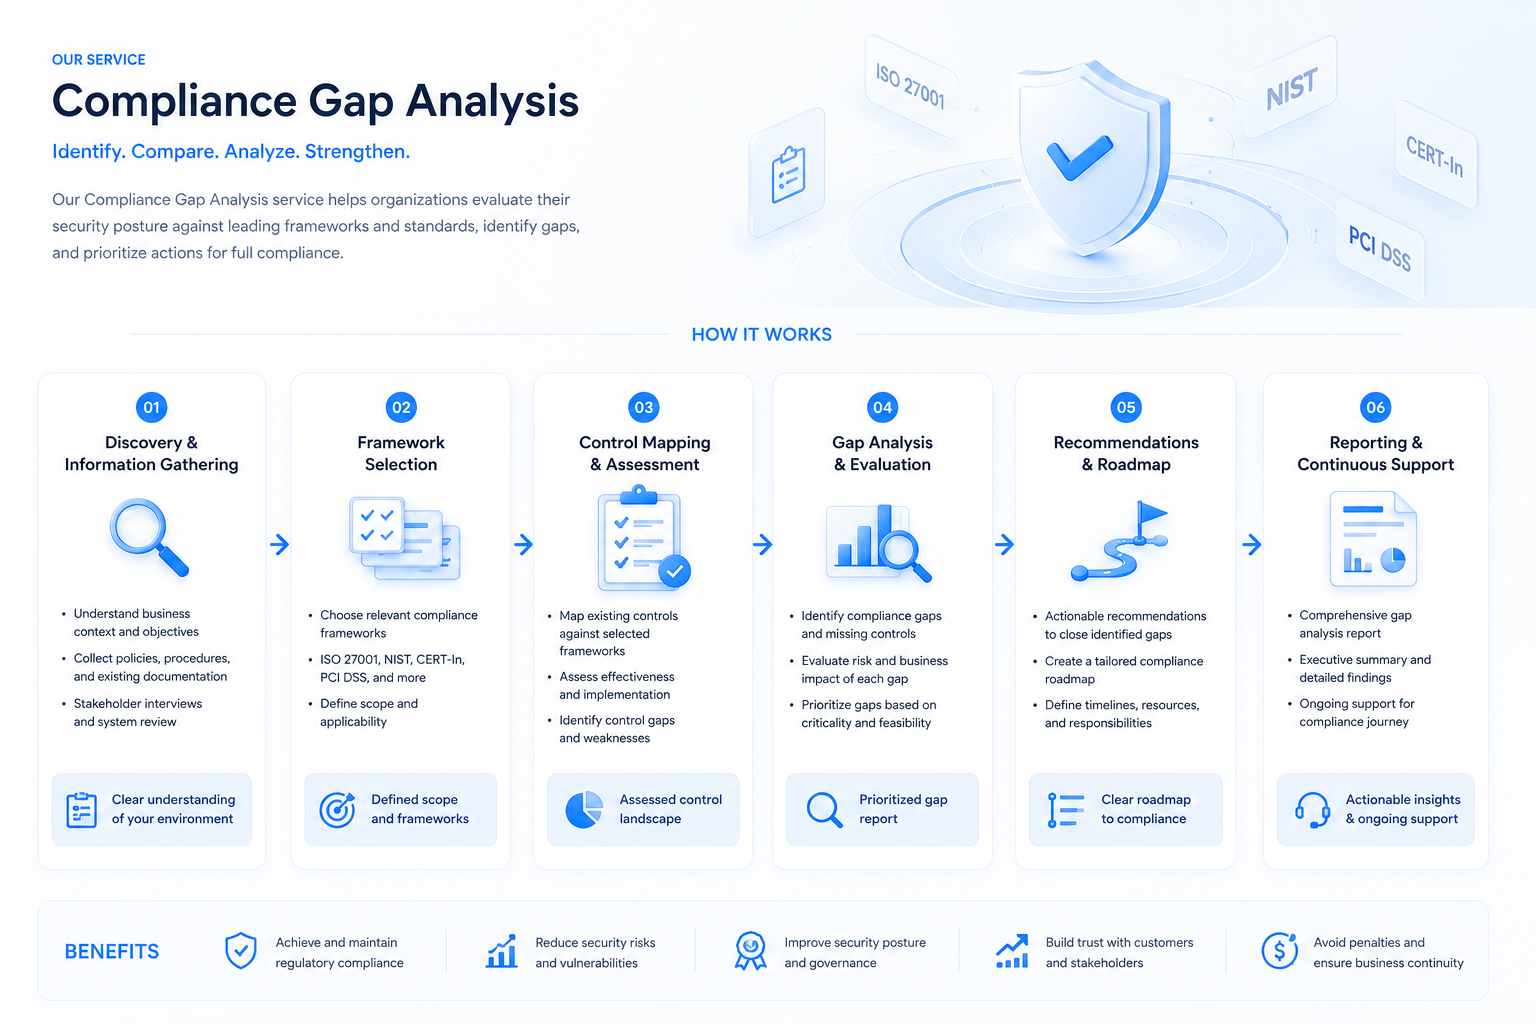
Gap Analysis
Assess compliance gaps against industry standards, regulatory requirements, and cybersecurity best practices.
Risk Prioritisation
Rank identified risks based on business impact, likelihood, and severity to focus remediation efforts effectively.
Remediation Roadmap
Receive a prioritised action plan with practical recommendations to strengthen your security posture.
Executive Reporting
Executive-level risk summary and technical findings designed for leadership, auditors, and security teams.
Service Walkthrough
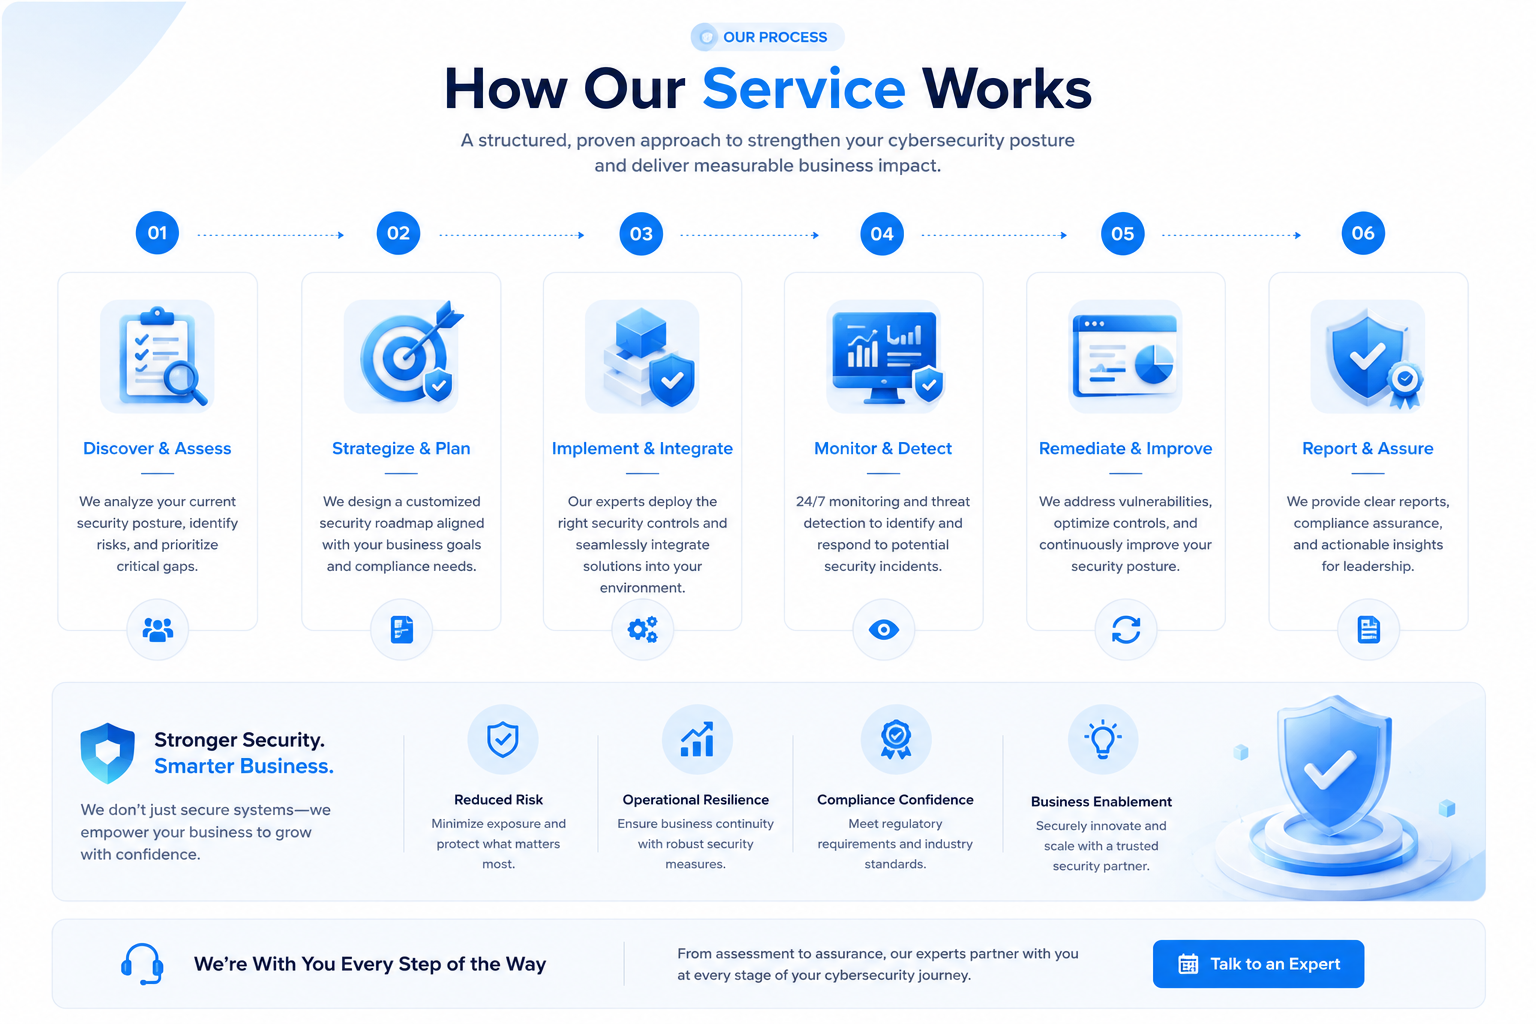
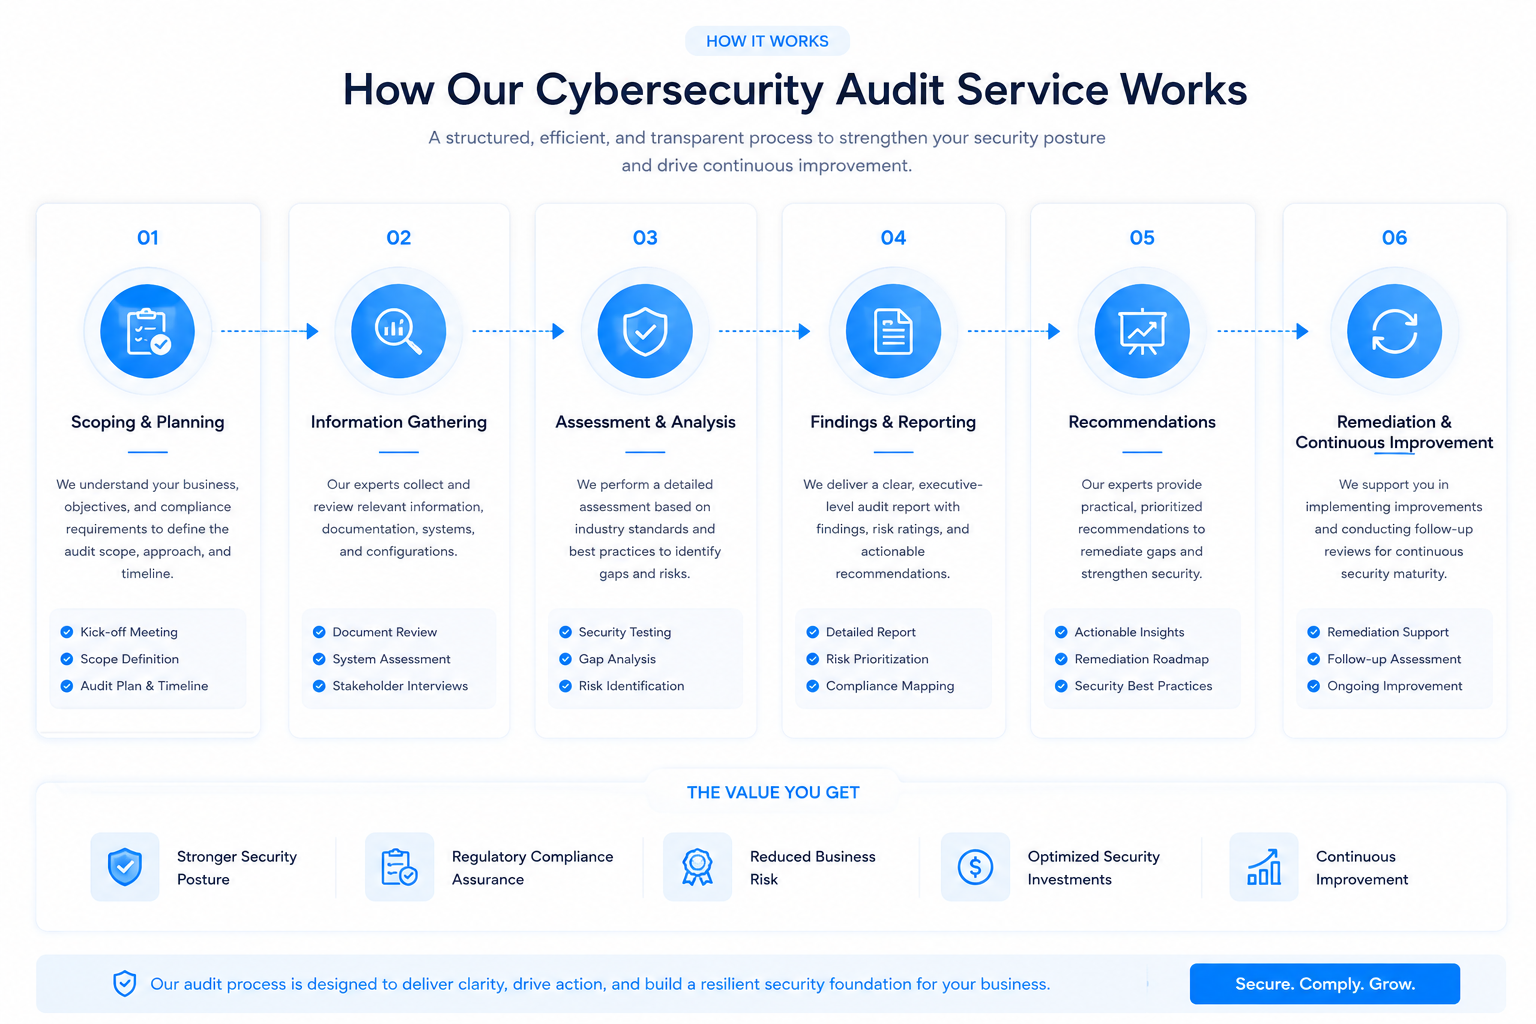
Cybersecurity Audit Process
Learn how MOBISEC evaluates your security posture, identifies critical gaps, and delivers a prioritized remediation roadmap.
The Value
Why Choose This Service
Know Before Attackers Do
Identify vulnerabilities in your environment before threat actors exploit them, reducing breach probability significantly.
Regulatory Confidence
Demonstrate compliance readiness to auditors and regulators with an independent, documented security assessment.
Informed Investment
Prioritise security spending based on real risk data — not assumptions — ensuring maximum return on security investment.
Expert Guidance
Benefit from MOBISEC's 18+ years of enterprise security expertise and sector-specific threat intelligence.
Our Approach
How We Deliver
Scoping & Discovery
Define audit scope, collect asset inventory, and align objectives with your business priorities and regulatory obligations.
Assessment & Analysis
Conduct technical vulnerability scanning, configuration reviews, policy analysis, and interview key stakeholders.
Risk Scoring
Score all findings by CVSS severity and business impact, creating a prioritised risk register for your organisation.
Reporting & Roadmap
Deliver executive and technical reports with a phased remediation roadmap, ownership matrix, and milestone tracking.
Industries
Who We Serve
Banking & Finance
RBI, SEBI, and PCI-DSS compliance-aligned security audits for financial institutions and fintech companies.
Government
CERT-In compliant security audits for government agencies protecting sensitive citizen and classified data.
Healthcare
DPDP and HIPAA-aligned security assessments for hospitals and health information systems.
Enterprise
ISO 27001 and NIST-aligned audits for large enterprises managing complex, distributed IT environments.