24/7 Security Operations
24/7 AI-Powered Security Operations Centre
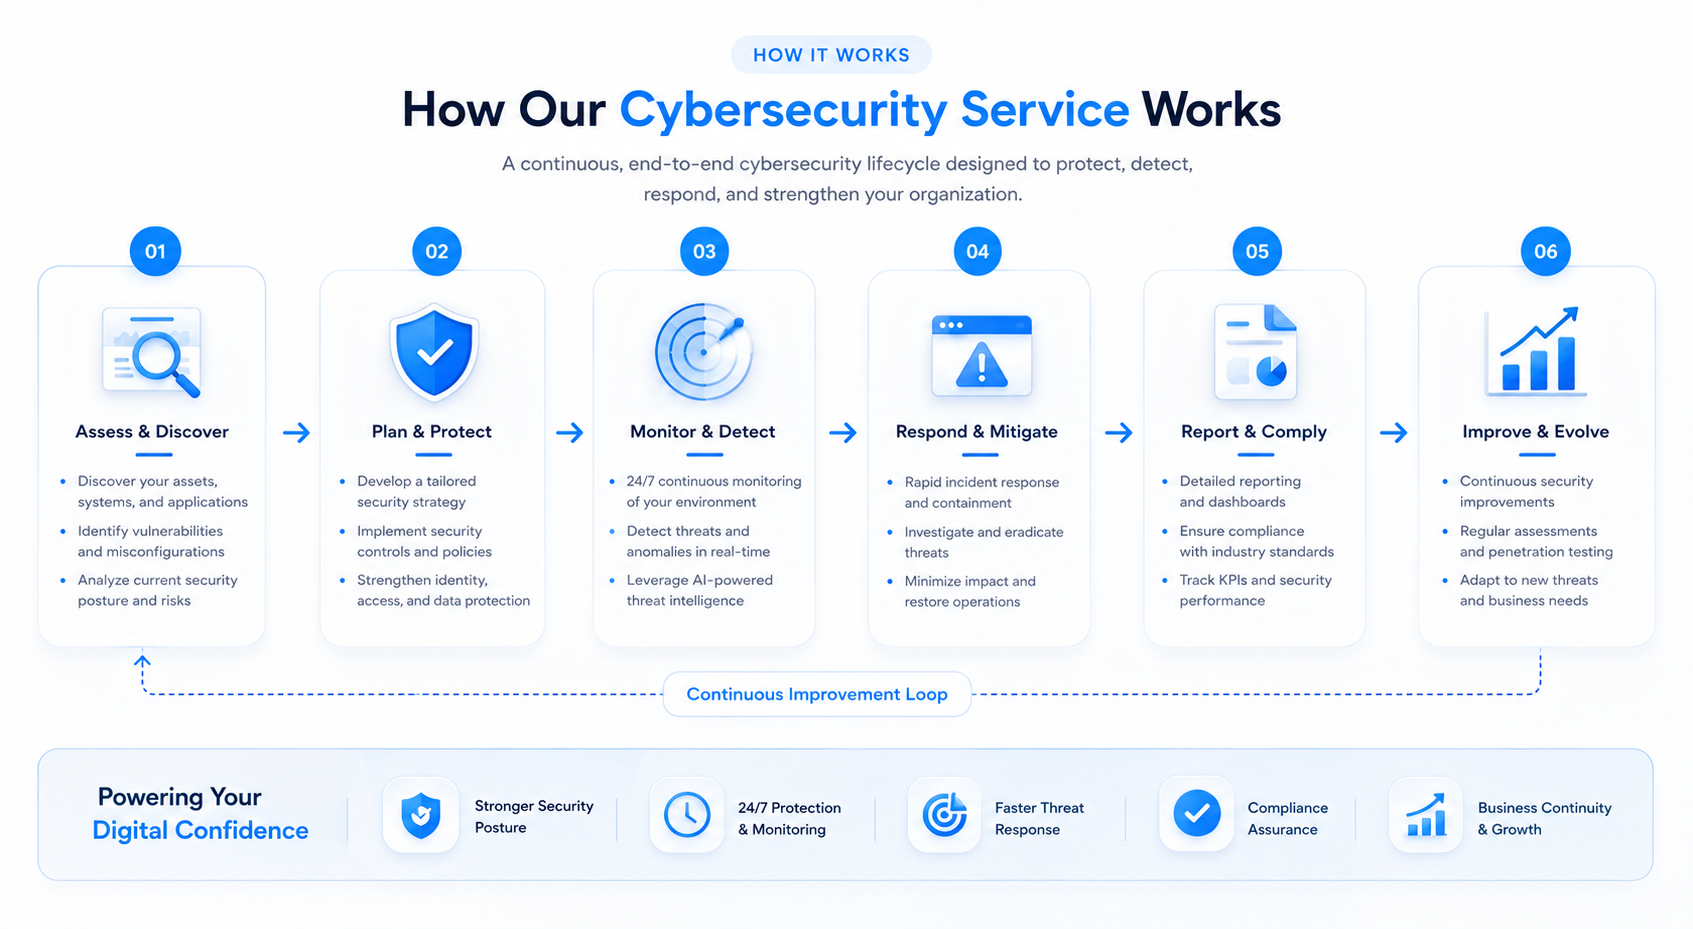
MOBISEC Managed SOC provides round-the-clock threat monitoring, detection, and response powered by AI-driven analytics and a team of certified security analysts. With a 15-minute incident response SLA and deep integration with your existing security stack, our SOC becomes an extension of your internal security team.
24/7/365 Threat Monitoring
Round-the-clock monitoring of security events, logs, and alerts by AI-driven systems and security analysts.
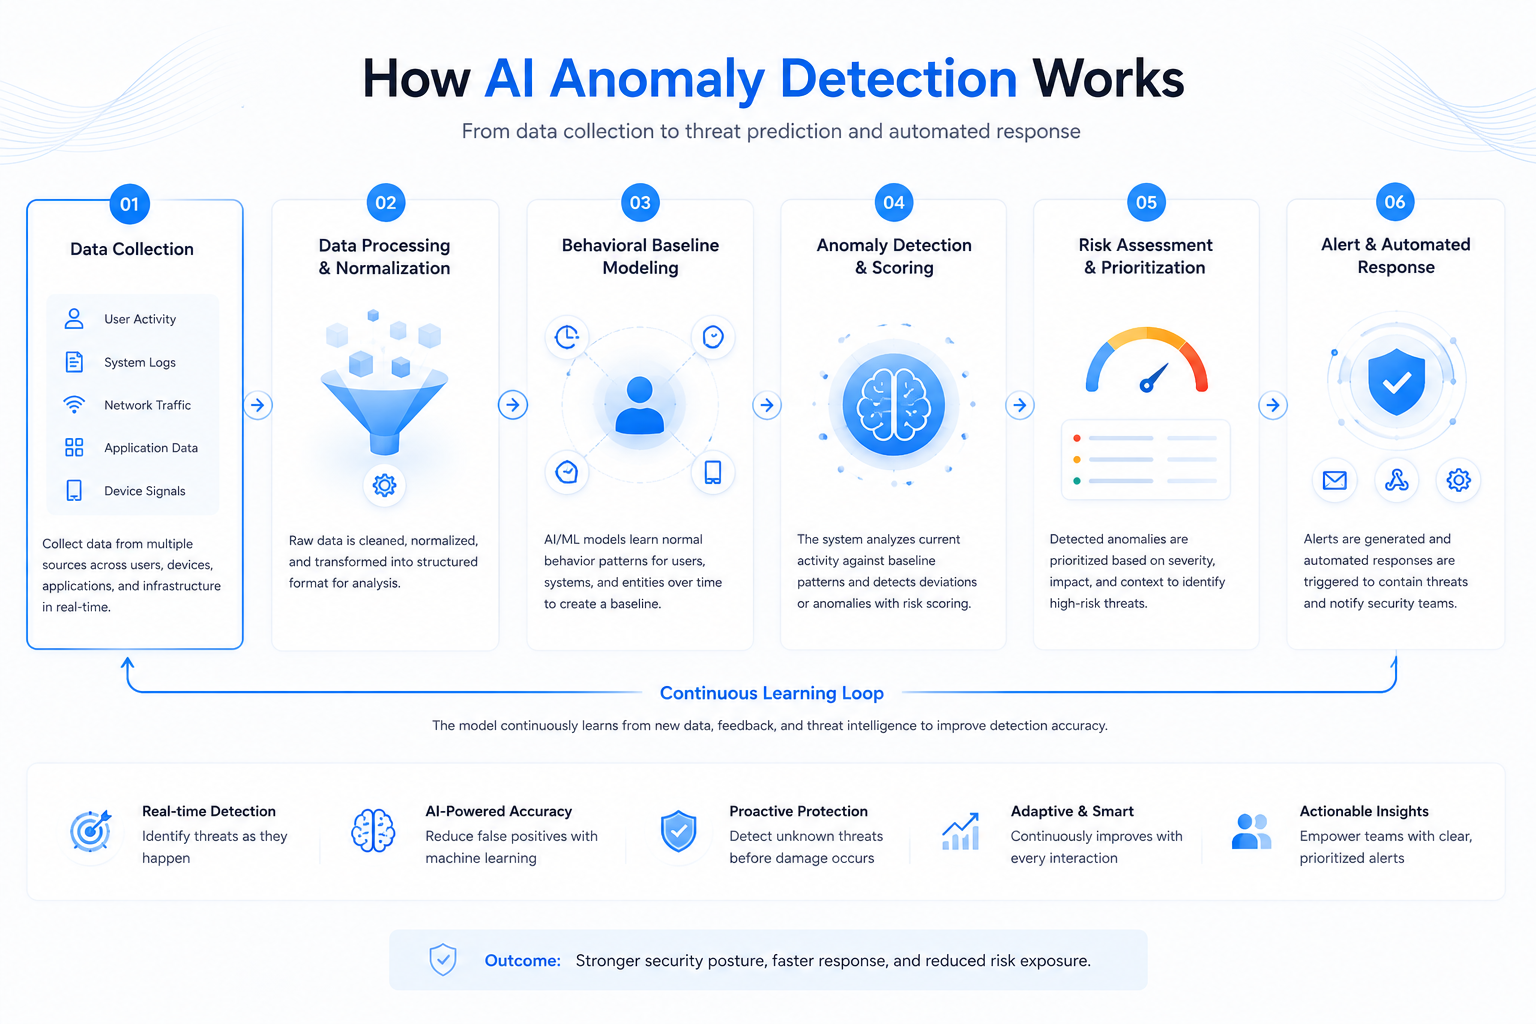
AI-Powered Anomaly Detection
Machine learning models detect suspicious behaviour, insider threats, and unknown attack patterns in real time.
Incident Response — <15 Min SLA
Guaranteed analyst engagement and incident response within 15 minutes for confirmed critical threats.
SIEM Integration
Seamless integration with existing SIEM, security tools, and ticketing platforms for centralised visibility.
Threat Intelligence Feeds
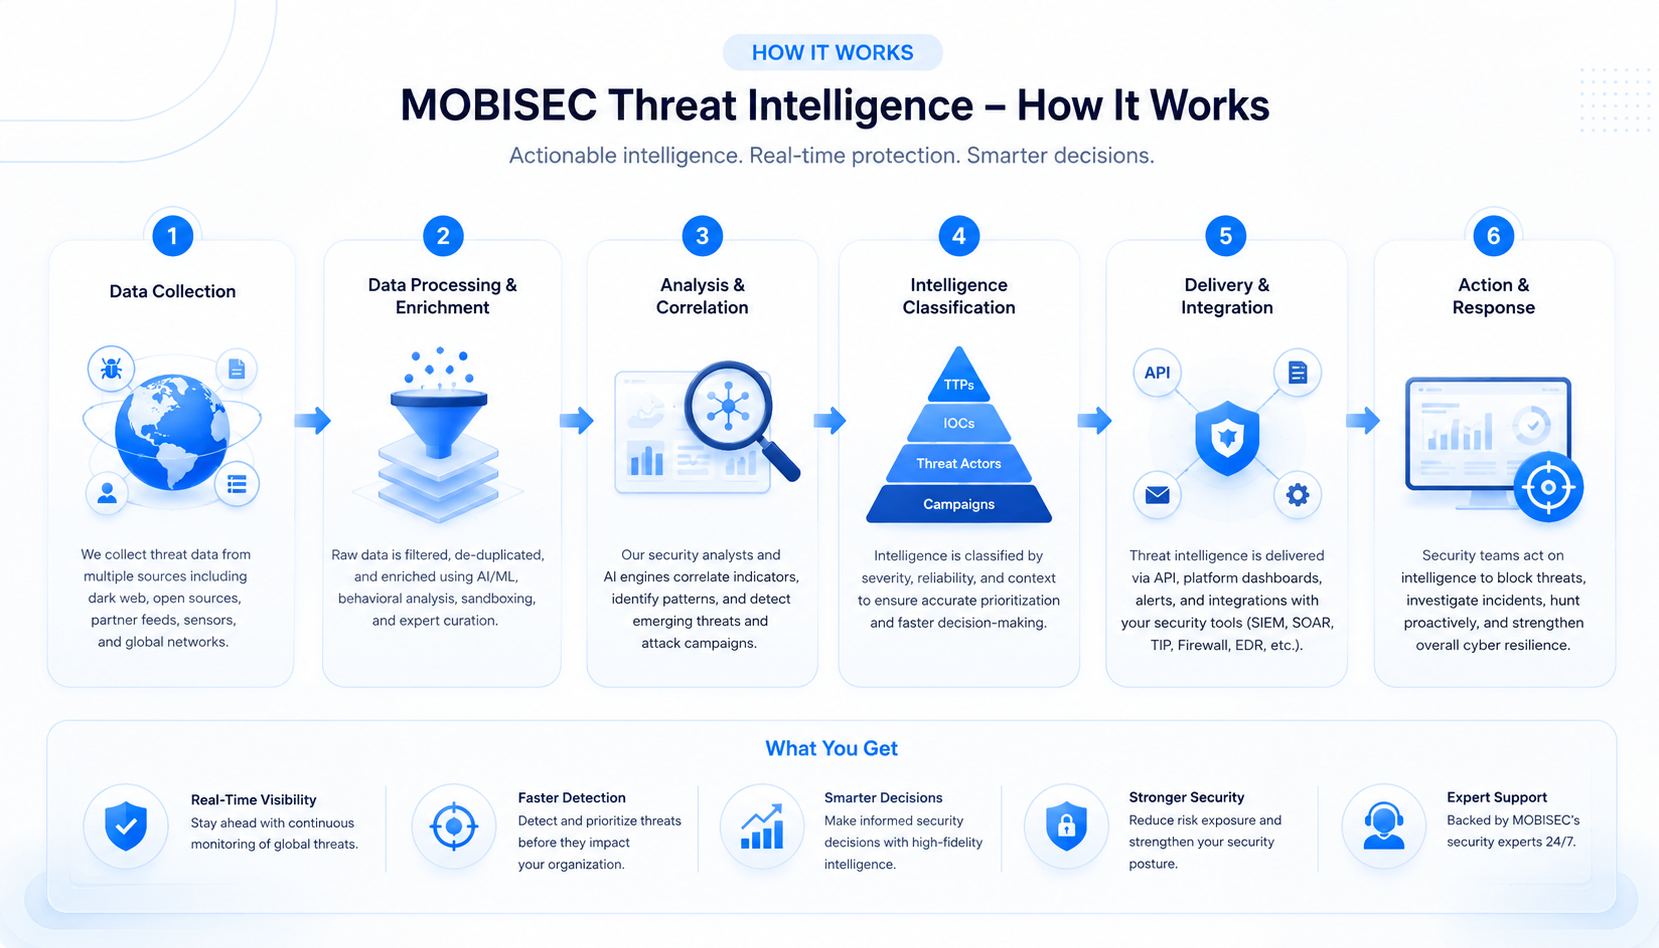
Enrich detections with actionable threat intelligence, indicators of compromise, and emerging threat data.
CISO Monthly Briefings
Executive-level threat intelligence reports, incident summaries, and strategic security recommendations.
Service Walkthrough
Managed SOC Overview
Discover how our AI-powered Security Operations Centre monitors, detects, and responds to threats 24/7.
The Value
Why Choose This Service
Always-On Coverage
Eliminate security blindspots during nights, weekends, and holidays — our SOC is always watching your environment.
Rapid Incident Containment
Sub-15-minute response means threats are contained before they escalate into major incidents.
AI-Augmented Analysis
AI dramatically reduces false positives, ensuring analysts focus on real threats and not noise.
Extend Your Team
Gain access to a full SOC team of L1, L2, and L3 analysts at a fraction of the cost of building in-house.
Our Approach
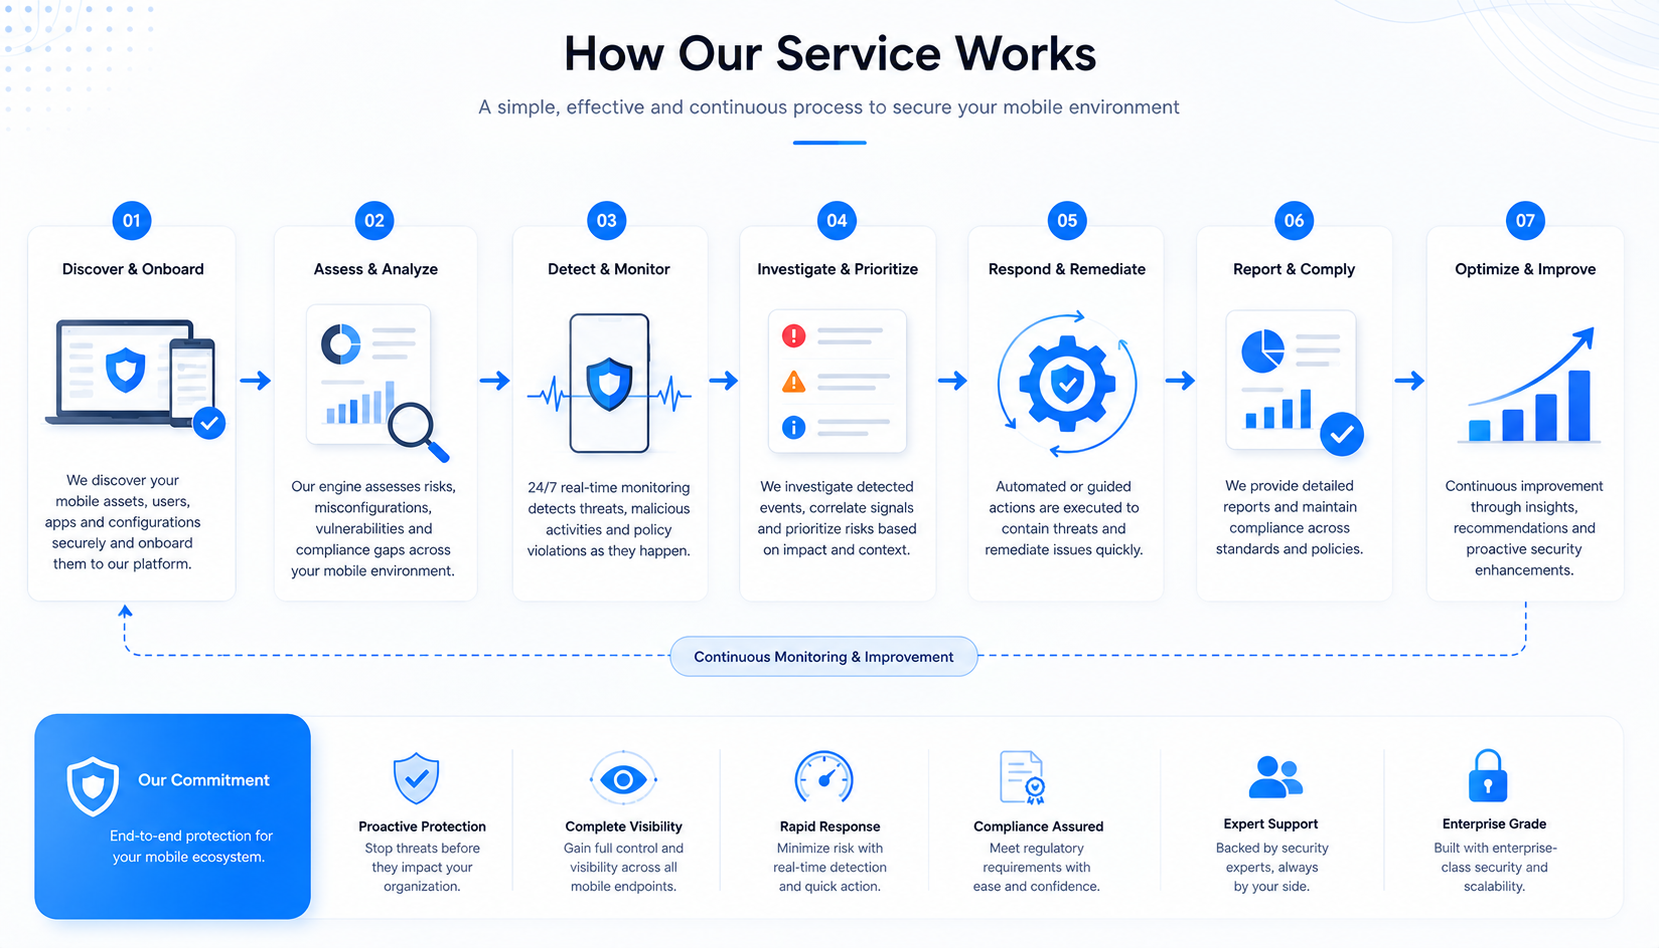
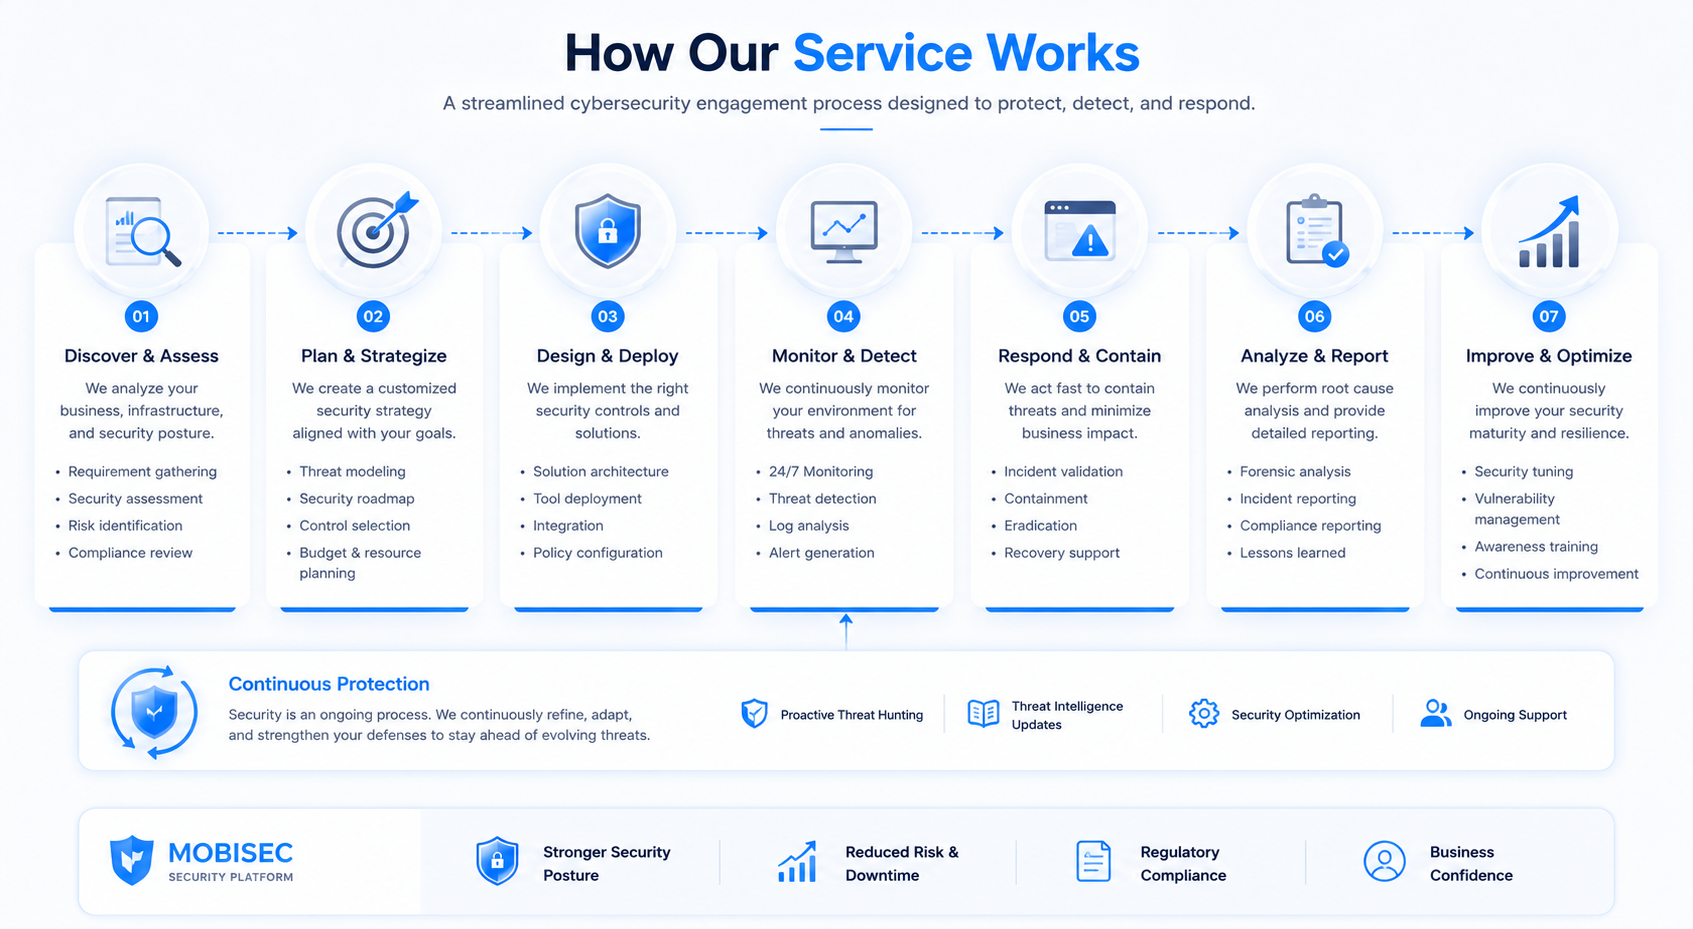
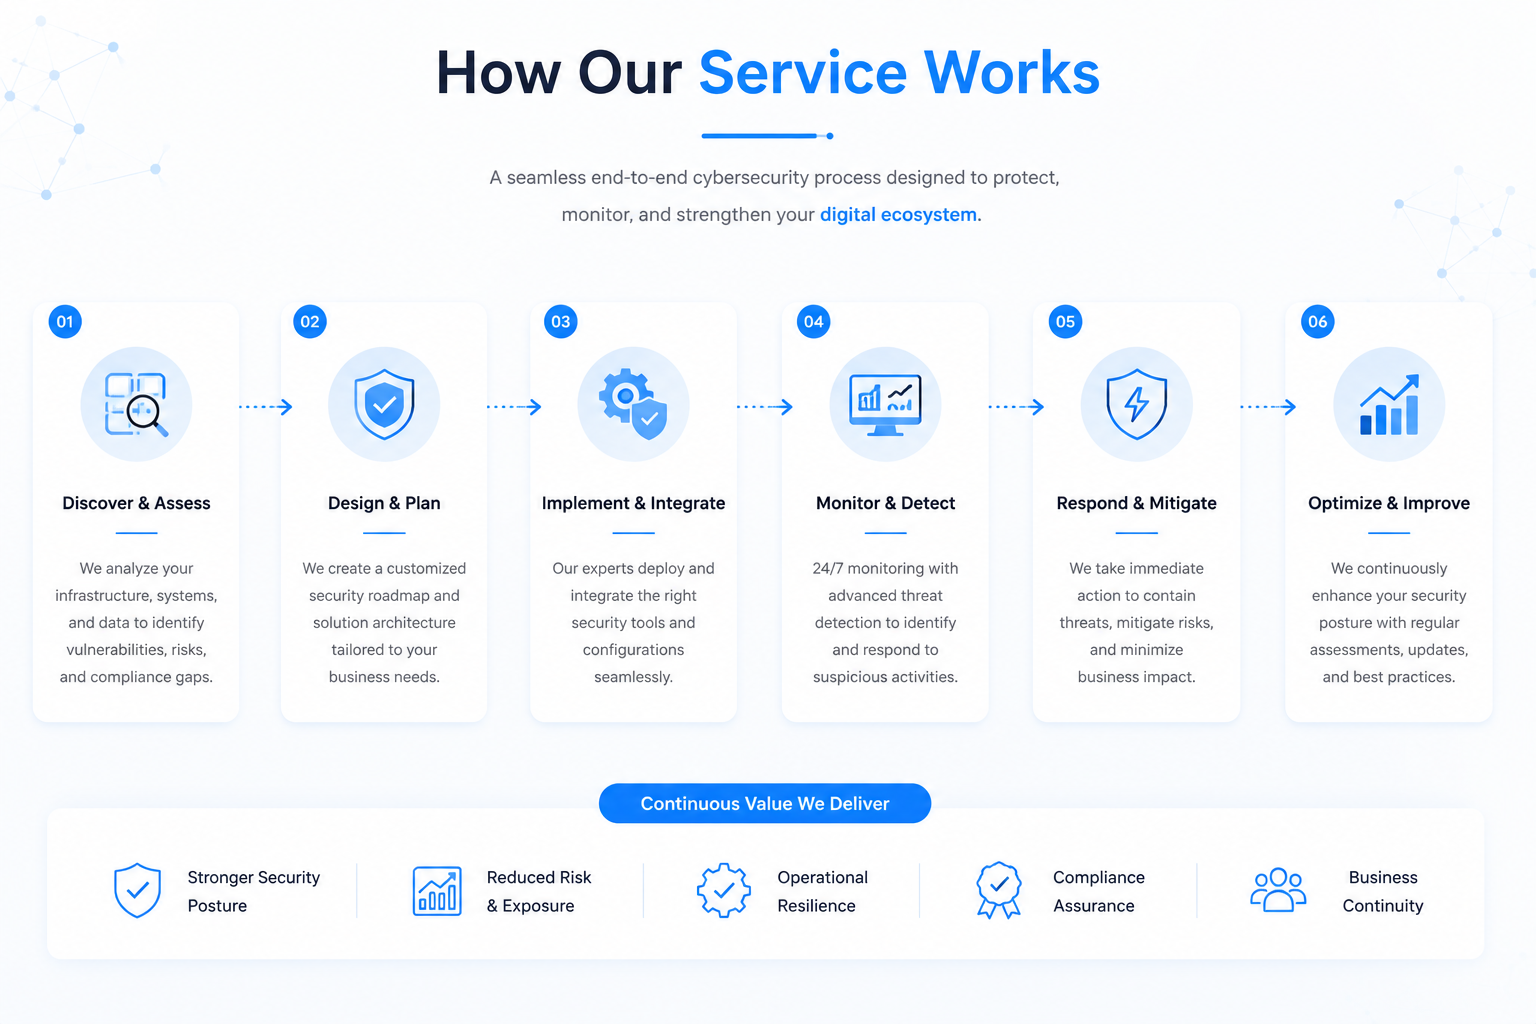
How We Deliver
Onboarding & Integration
Connect your security tools, deploy log collectors, and configure your SIEM integration within days, not months.
Baseline & Tuning
Establish environment baselines, reduce false positives, and tune detection rules to your specific infrastructure.
Continuous Monitoring
AI and analyst teams monitor all event streams 24/7, triaging alerts and escalating confirmed threats immediately.
Response & Reporting
Execute incident response playbooks, contain threats, and deliver post-incident reports with root cause analysis.
Industries
Who We Serve
Banking & Finance
24/7 SOC coverage for financial institutions with RBI-aligned incident reporting and financial malware detection.
Government
Classified-grade SOC monitoring for government agencies with secure, sovereign data handling.
Enterprise
Full-spectrum SOC-as-a-Service for enterprises that want enterprise-grade security without the overhead of building in-house.
Healthcare
SOC coverage protecting patient data and clinical operations from ransomware and healthcare-targeted threat actors.