Vulnerability Assessment & Penetration Testing
Find Every Vulnerability Before Attackers Do
MOBISEC VAPT combines automated vulnerability scanning with expert-led manual penetration testing to identify security weaknesses across your mobile applications, web platforms, APIs, and enterprise infrastructure. Every engagement delivers CVSS-scored findings with proof-of-concept evidence and retest validation.
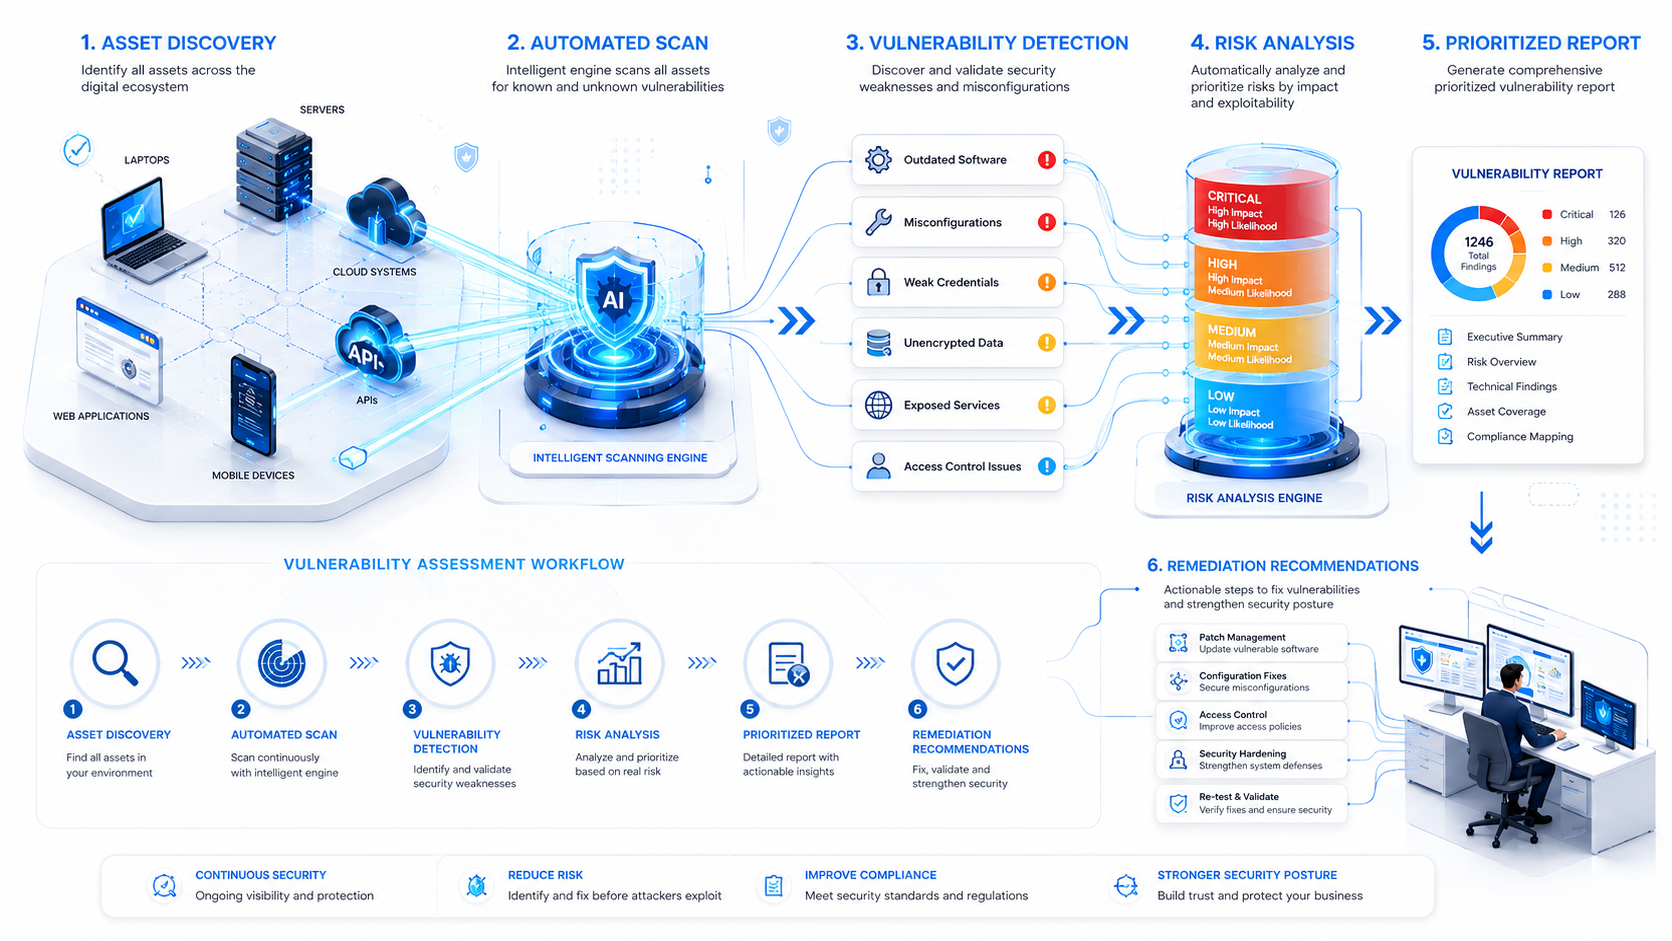
Vulnerability Assessment
Automated and manual assessment to identify weaknesses across applications, APIs, networks, and infrastructure.
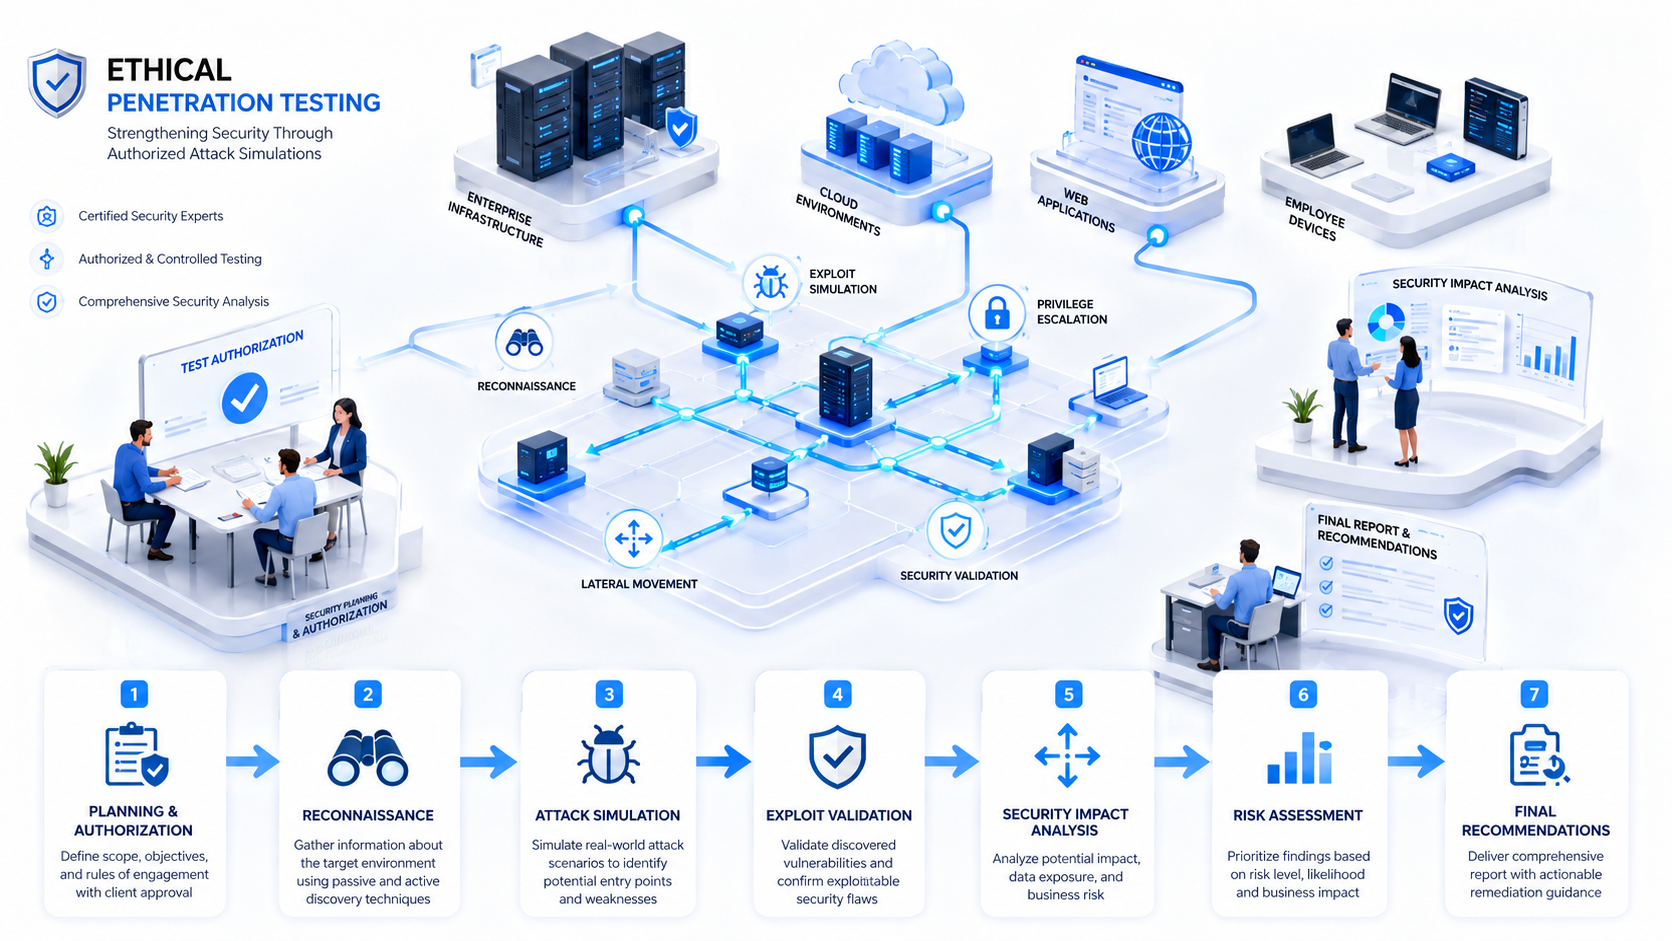
Penetration Testing
Simulated real-world attacks to validate vulnerabilities and determine their actual exploitability.
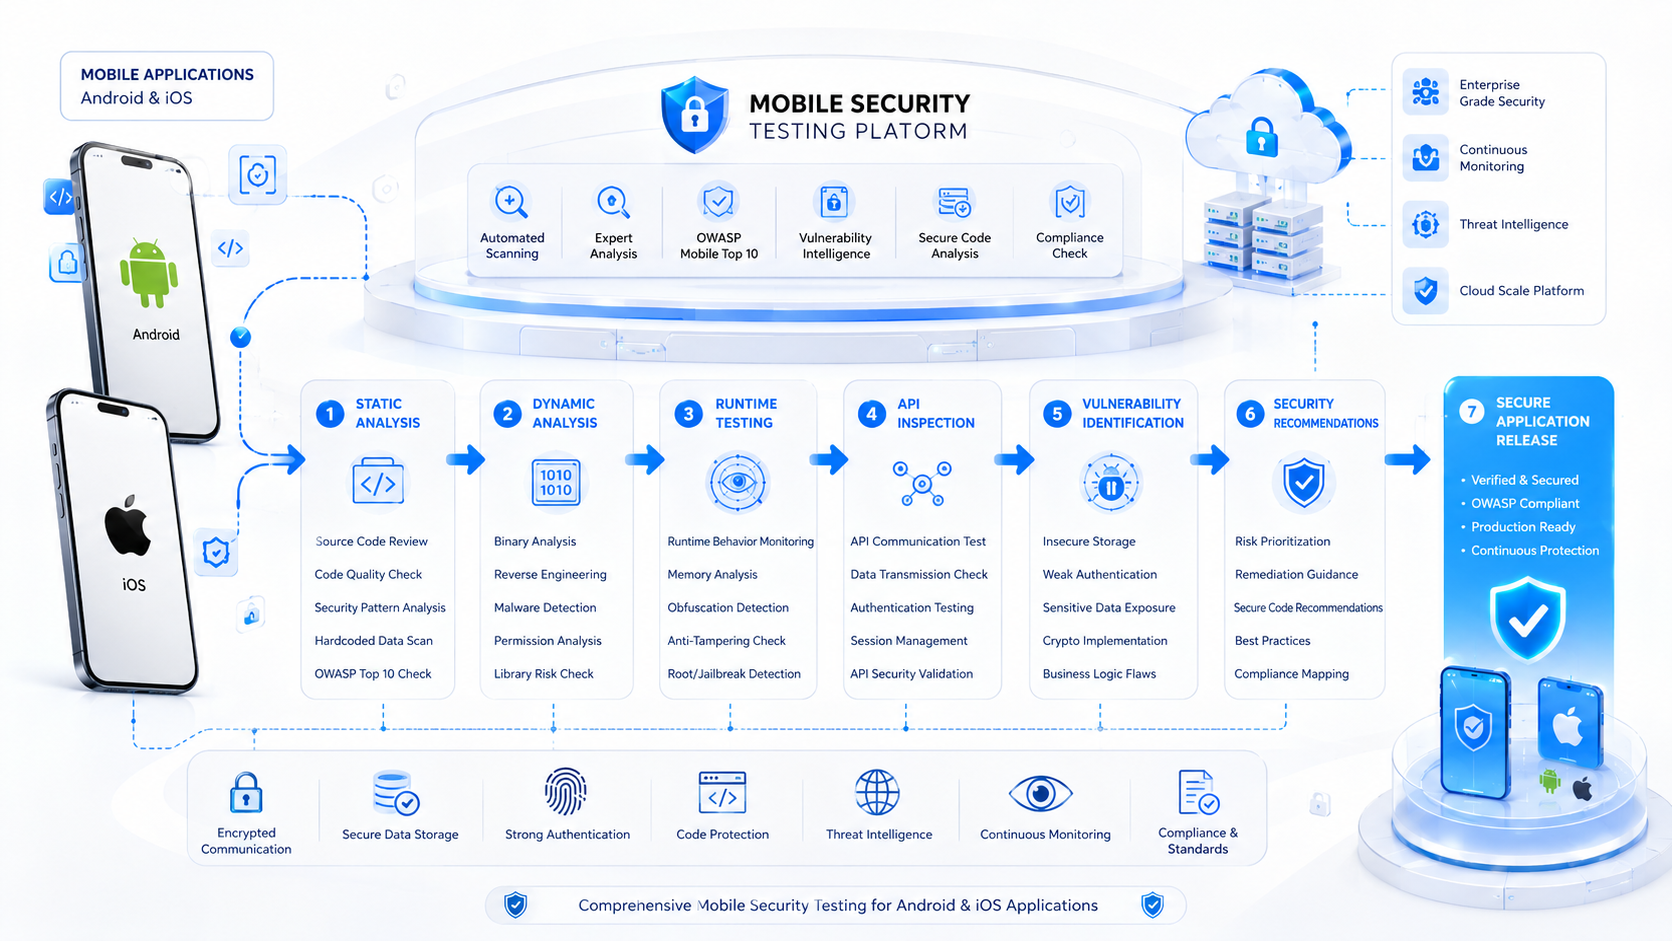
Mobile App Testing
Comprehensive security testing of Android and iOS applications using OWASP Mobile Security standards.
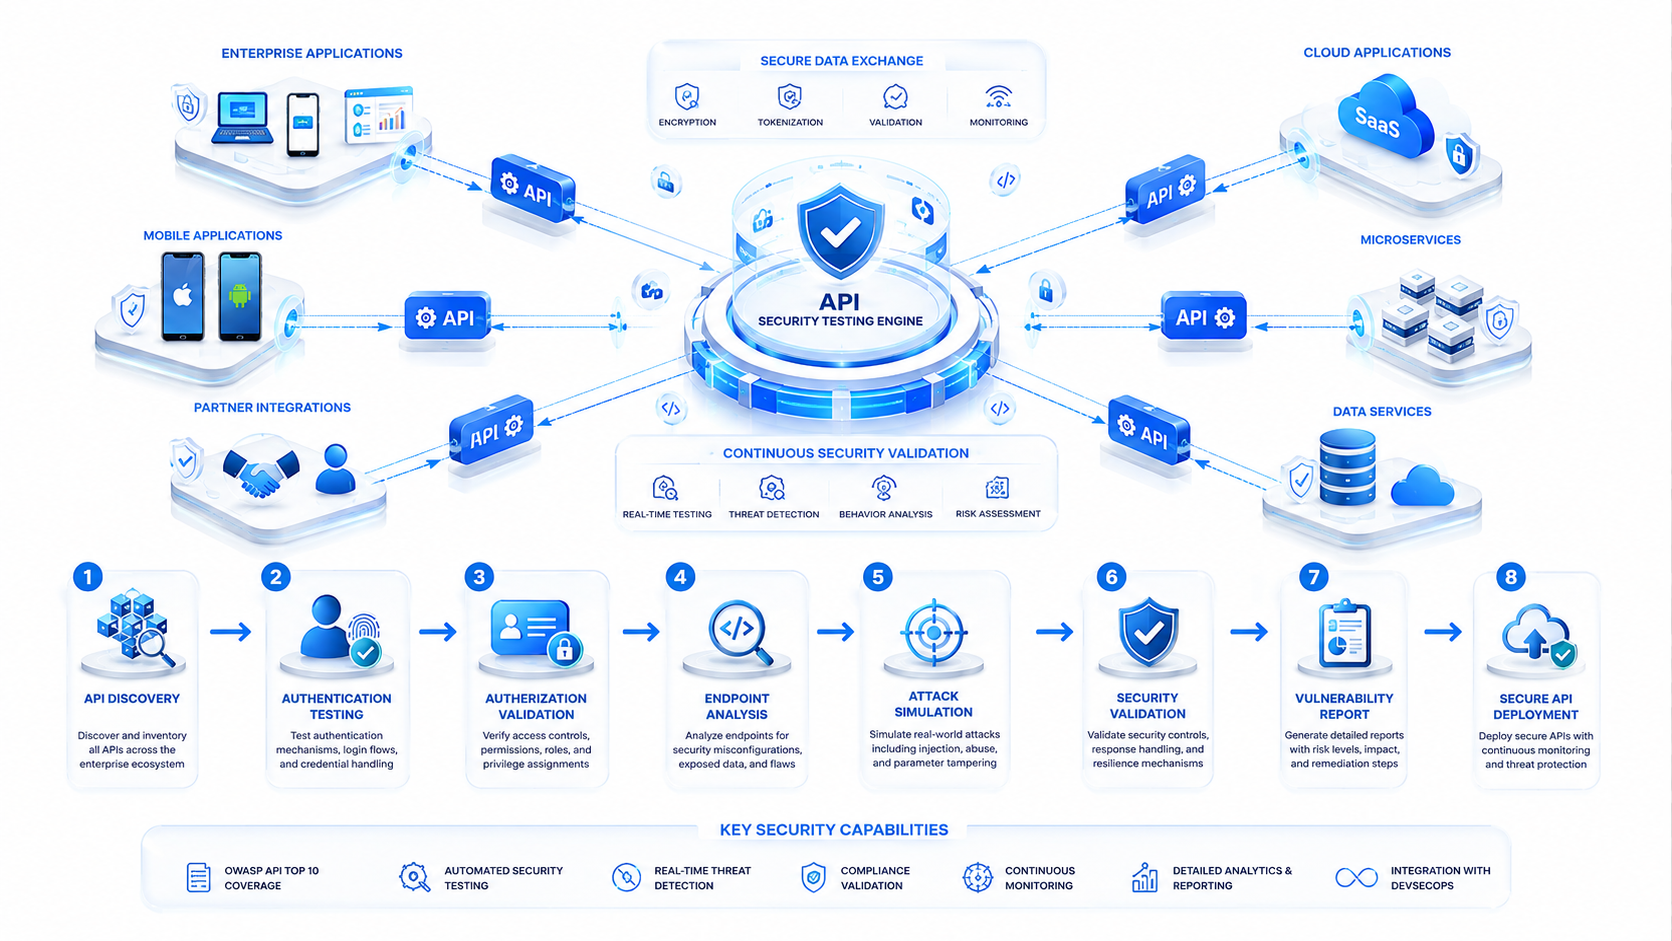
API Security Testing
Assess authentication, authorization, data exposure, and business logic vulnerabilities in APIs.
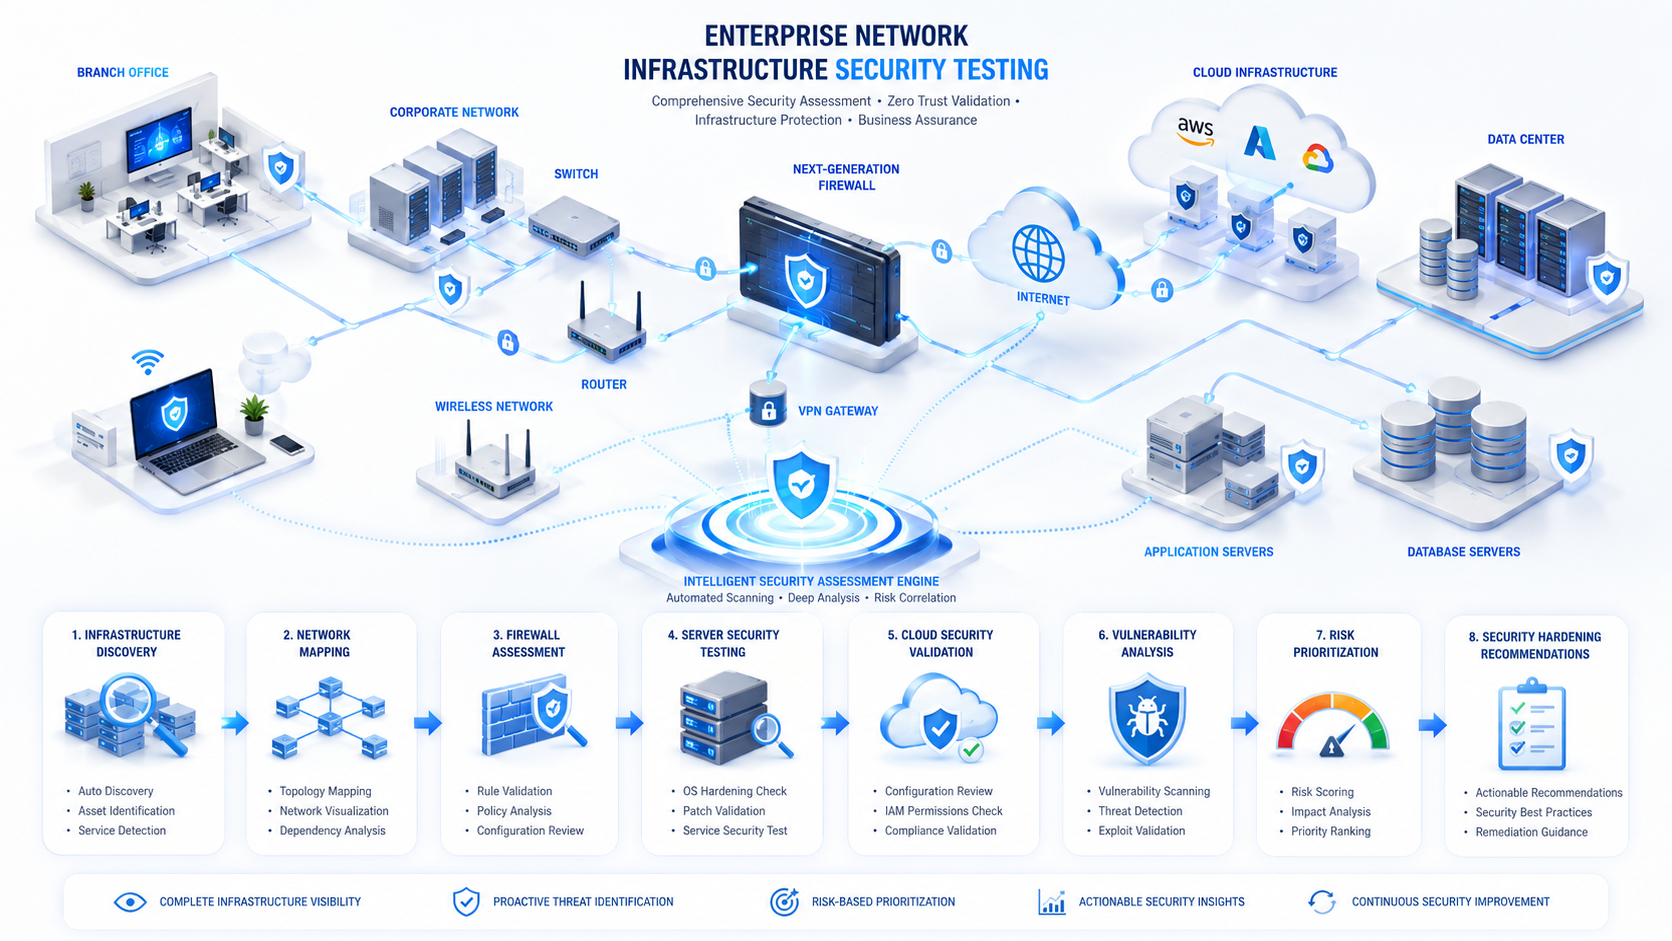
Network Infrastructure Testing
Evaluate servers, firewalls, cloud environments, and internal networks for exploitable weaknesses.
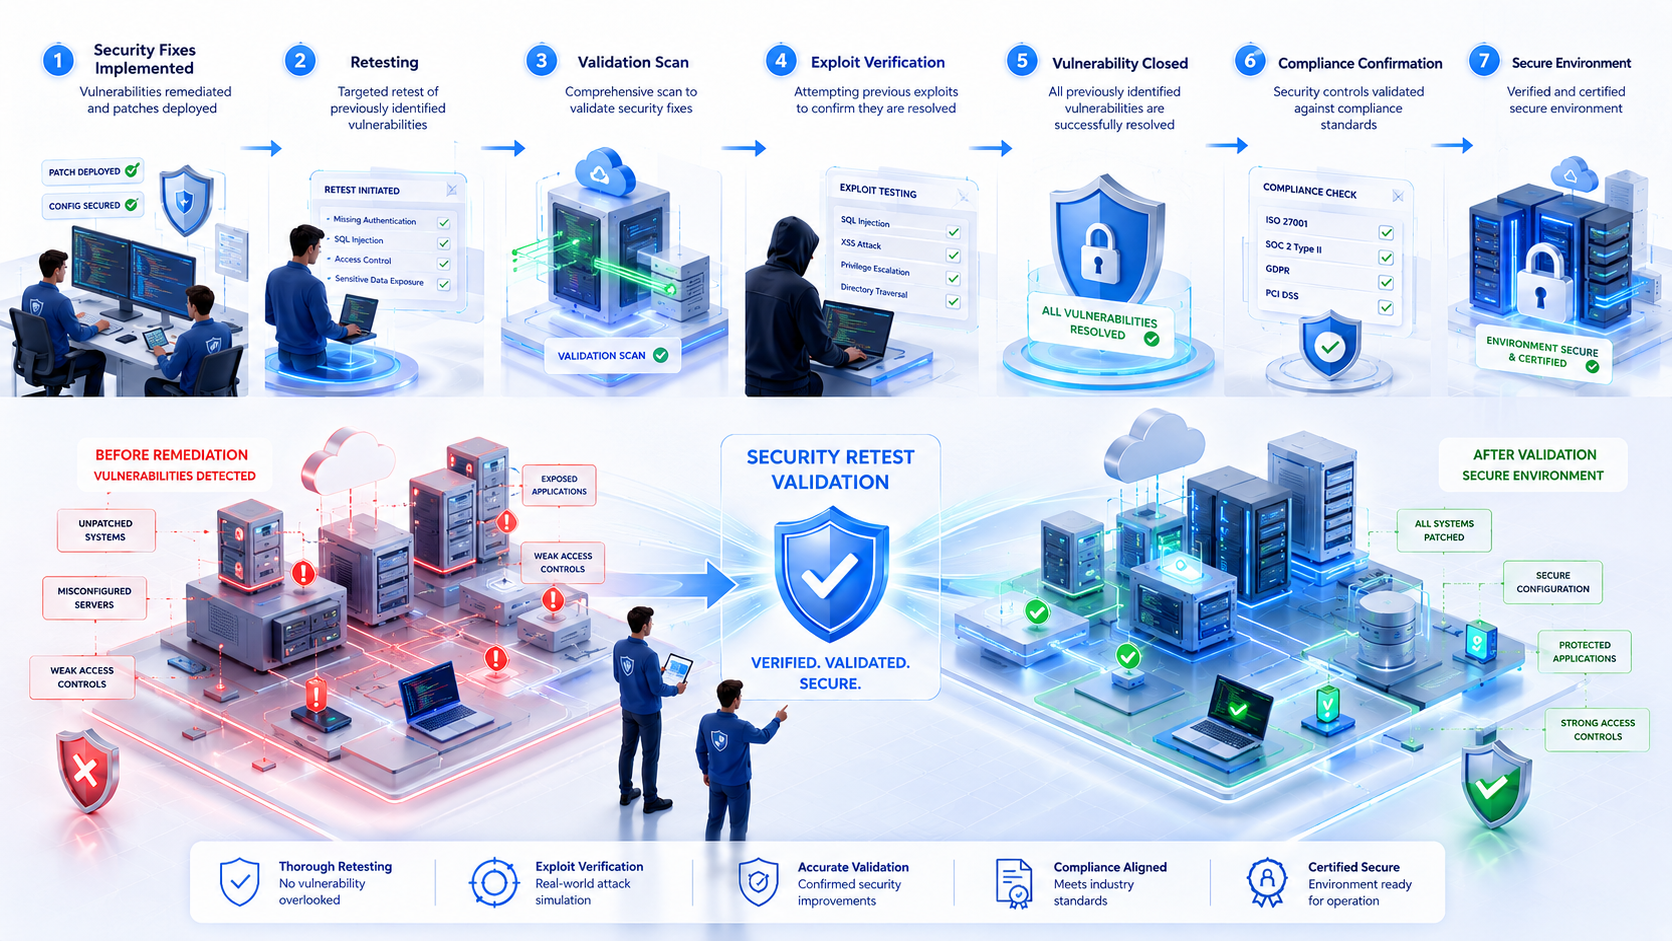
Retest & Validation
Validate remediation efforts and confirm that identified vulnerabilities have been successfully resolved.
Service Walkthrough
VAPT Assessment Walkthrough
See how our experts uncover vulnerabilities across applications, APIs, networks, and infrastructure before attackers do.
The Value
Why Choose This Service
Real Attacker Perspective
Understand exactly how an attacker would exploit your systems — not just what vulnerabilities exist, but how they chain together.
Compliance-Ready Evidence
VAPT reports map findings to PCI-DSS, ISO 27001, and CERT-In controls for audit and regulatory submission.
Fast Turnaround
Structured delivery with initial findings within 72 hours and final reports within 7 business days of testing completion.
Validated Remediation
Free retest ensures your fixes actually work — we validate every critical and high finding post-remediation.
Our Approach
How We Deliver
Scoping & Rules of Engagement
Define test scope, safe hours, emergency contacts, and rules of engagement to ensure a safe, controlled engagement.
Reconnaissance & Scanning
Passive and active reconnaissance combined with vulnerability scanning to build a comprehensive target profile.
Exploitation & Validation
Controlled exploitation of confirmed vulnerabilities with proof-of-concept evidence demonstrating real business impact.
Reporting & Retest
Detailed CVSS-scored report, executive summary, remediation guidance, and free retest of all critical/high findings.
Industries
Who We Serve
Banking & Fintech
PCI-DSS compliant VAPT for banking apps, payment gateways, and financial data processing systems.
Enterprise
Comprehensive infrastructure and application VAPT for large enterprises with complex hybrid environments.
Government
CERT-In mandated VAPT for government web services, citizen portals, and critical national infrastructure.
Healthcare
VAPT for electronic health record systems, patient portals, and connected medical device platforms.